How each part is protected
Eight controls that apply to every workspace, every day, with nothing to switch on.
Send-only Gmail access
Google is asked for the send permission and your address, nothing else. Pedibee cannot read, search or delete anything in your inbox.
Encrypted refresh tokens
The token Google issues for sending is stored encrypted with AES-256-GCM. If Google revokes it, sending stops instead of failing silently.
API keys stored as hashes
A key is shown once. Pedibee keeps only its SHA-256 hash, and keys carry scopes, can expire and stop when their creator leaves.
OAuth 2.1 for assistants
Assistants connect with OAuth 2.1 and PKCE. Access tokens last an hour, refresh tokens rotate on every use, and revoking ends it at once.
Signed links
Every open pixel, click and unsubscribe link carries an HMAC signature, so nobody can forge an open, a click or an opt-out.
Per-workspace isolation
Every record belongs to one workspace and every query is filtered by it. Removing someone ends their access immediately.
Owner, manager, member
Members read. Managers change data, send and run the team. Only the owner deletes the workspace or sets up tracking.
Google Cloud and Cloudflare
The API runs on Google Cloud. Your tracking domain is served through Cloudflare, which issues its certificate.
The rules that run every day
Your account
- Work emails only: public providers and disposable domains cannot sign up.
- Passwords are hashed with bcrypt. Five failed sign-ins lock the account for fifteen minutes.
- Sign-in, sign-up and reset links are rate limited per address and per IP.
- Logging out signs out every device, and no session lives longer than thirty days.
- Writes from any site other than the dashboard are refused before any work is done.
Your recipients
- Campaign, sequence and one-off mail carries a visible unsubscribe link and a one-click unsubscribe header. Transactional automations are the only exception.
- Opening an unsubscribe link only shows a confirmation page, so link scanners cannot opt your contacts out.
- Every opt-out lands on a do-not-email list that every send checks, including the API and assistants.
- Tracking runs only on a subdomain of your own domain. Without one, emails go out untracked.
- Pedibee never rotates sending addresses or domains to get past filters.
Access you choose, checked on every call
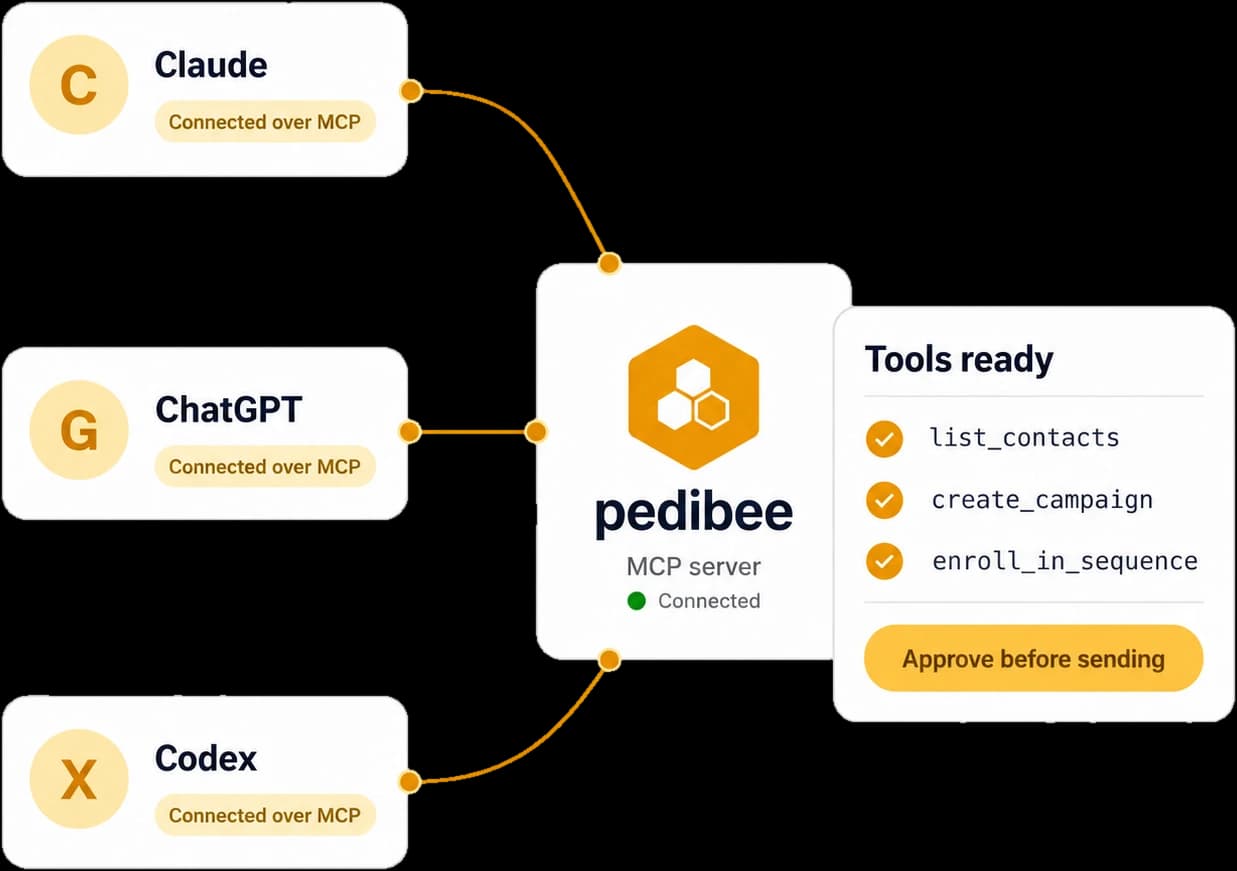
An assistant connects with a button and gets a connection scoped to one workspace, with access capped at your role. A key for your own servers gets explicit read, write and send scopes.
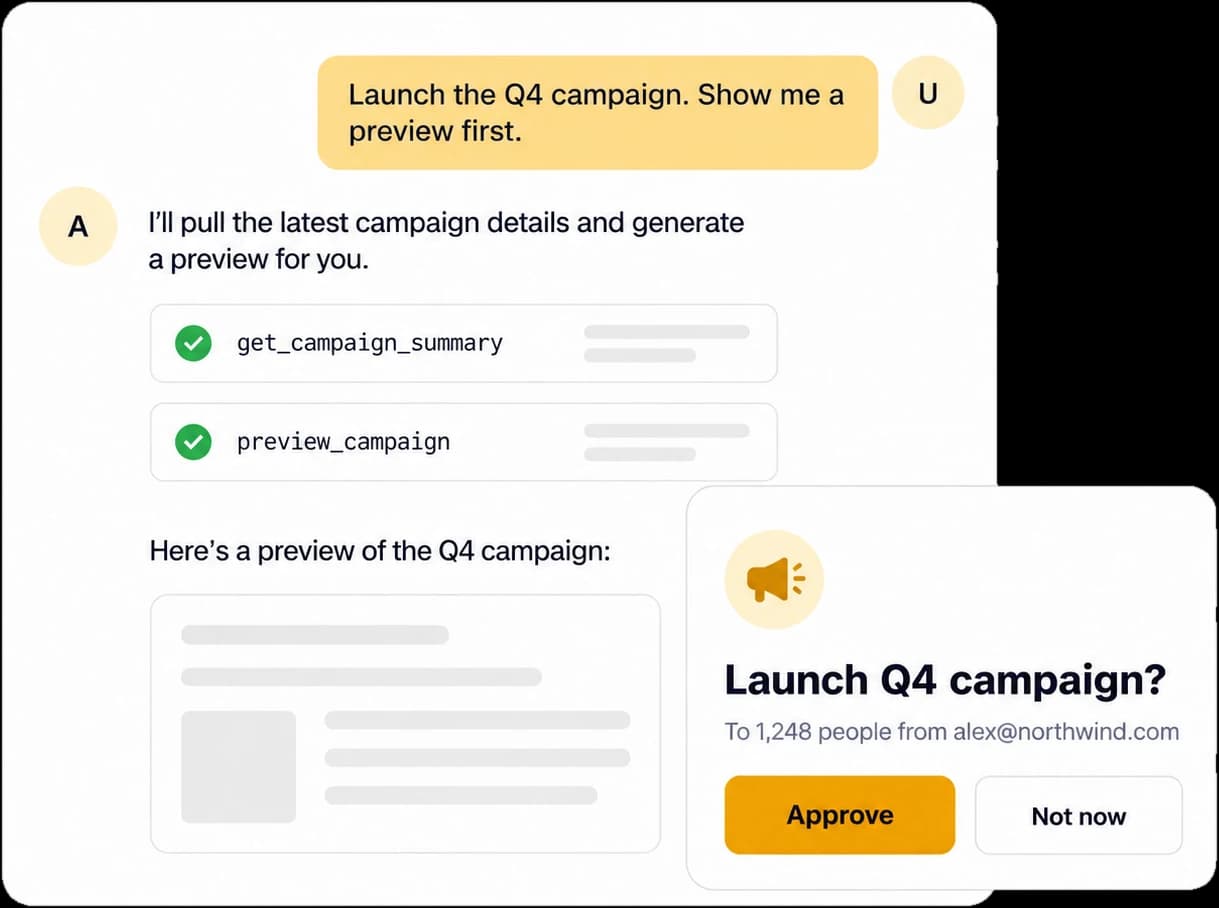
Both are checked on every call, rate limited, and end the moment you revoke them or leave the workspace. The MCP server tells assistants to treat anything it returns as data, never as instructions, and marks sends and deletes so they confirm with you first.
Found something? Tell us first.
Email what you found, how to reproduce it and its impact. A person replies and keeps you informed while we fix it. Test only against accounts and workspaces you own. security@pedibee.com